Dynamic Storage Provisioning ?
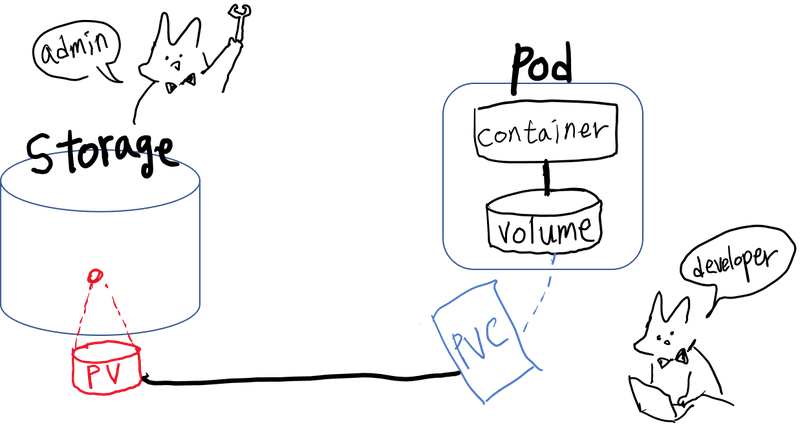
전체 구성 👾
vi serviceaccount.yaml
apiVersion: v1
kind: ServiceAccount
metadata:
name: nfs-provisioner
kubectl apply -f serviceaccount.yaml
kind: ClusterRole
apiVersion: rbac.authorization.k8s.io/v1
metadata:
name: nfs-provisioner-runner
rules:
- apiGroups: [""]
resources: ["persistentvolumes"]
verbs: ["get", "list", "watch", "create", "delete"]
- apiGroups: [""]
resources: ["persistentvolumeclaims"]
verbs: ["get", "list", "watch", "update"]
- apiGroups: ["storage.k8s.io"]
resources: ["storageclasses"]
verbs: ["get", "list", "watch"]
- apiGroups: [""]
resources: ["events"]
verbs: ["watch", "create", "update", "patch"]
- apiGroups: [""]
resources: ["services", "endpoints"]
verbs: ["get"]
- apiGroups: ["extensions"]
resources: ["podsecuritypolicies"]
resourceNames: ["nfs-provisioner"]
verbs: ["use"]
kubectl apply -f clusterrole.yaml
kind: ClusterRoleBinding
apiVersion: rbac.authorization.k8s.io/v1
metadata:
name: run-nfs-provisioner
subjects:
- kind: ServiceAccount
    name: nfs-provisioner
    namespace: default
roleRef:
kind: ClusterRole
  name: nfs-provisioner-runner
  apiGroup: rbac.authorization.k8s.io

---
apiVersion: rbac.authorization.k8s.io/v1
kind: Role
metadata:
name: nfs-provisioner-otherRoles
rules:
- apiGroups: [""]
resources: ["endpoints"]
verbs: ["get", "list", "watch", "create", "update", "patch"]
---
apiVersion: rbac.authorization.k8s.io/v1
kind: RoleBinding
metadata:
name: nfs-provisioner-otherRoles
subjects:
- kind: ServiceAccount
    name: nfs-provisioner
    namespace: default    # provisioner가 배포될 네임스페이스
roleRef:
kind: Role
  name: nfs-provisioner-otherRoles
  apiGroup: rbac.authorization.k8s.io
kubectl apply -f clusterbinding.yaml
kind: Deployment
apiVersion: apps/v1
metadata:
name: nfs-client-provisioner
spec:
replicas: 1
strategy:
type: Recreate
  selector:
matchLabels:
app: nfs-client-provisioner
  template:
metadata:
labels:
app: nfs-client-provisioner
    spec:
serviceAccount: nfs-provisioner
      containers:
- name: nfs-client-provisioner
          image: registry.cn-hangzhou.aliyuncs.com/open-ali/nfs-client-provisioner
          volumeMounts:
- name: nfs-client-root
              mountPath: /persistentvolumes
          env:
- name: PROVISIONER_NAME
value: fuseim.pri/ifs
            - name: NFS_SERVER
value: 10.0.1.20
- name: NFS_PATH
value: /data/NFS
volumes:
- name: nfs-client-root
          nfs:
server: 10.0.1.20
path: /data/NFS
kubectl apply -f deployment-nfs.yaml
apiVersion: storage.k8s.io/v1beta1
kind: StorageClass
metadata:
name: managed-nfs-storage
provisioner: fuseim.pri/ifs
kubectl apply -f storageclass-nfs.yaml
apiVersion: apps/v1
kind: StatefulSet
metadata:
name: web
spec:
serviceName: "nginx1"
replicas: 1
selector:
matchLabels:
app: nginx1
  volumeClaimTemplates:
- metadata:
name: test
      annotations:
        volume.beta.kubernetes.io/storage-class: "managed-nfs-storage"
spec:
accessModes: [ "ReadWriteOnce" ]
resources:
requests:
storage: 2Gi
  template:
metadata:
labels:
app: nginx1
    spec:
serviceAccount: nfs-provisioner
     containers:
- name: nginx1
       image: nginx:1.7.9
volumeMounts:
- mountPath: "/mnt"
name: test
kubectl apply -f statefulset-nfs.yaml
kubectl get all
======
NAME READY STATUS RESTARTS AGE
pod/nfs-pod-provisioner-5f8686f8dd-bfkgz 1/1 Running 0 8m51s
apiVersion: v1
kind: PersistentVolumeClaim
metadata:
name: nfs-pvc-test
spec:
storageClassName: managed-nfs-storage # StorageClass 명
  accessModes:
- ReadWriteMany # 생성될 PV에 적용할 사용 모드
  resources:
requests:
storage: 10Mi  # 생성될 PV 크기
ReadWriteOnce (RWO): 하나의 Pod에만 마운트되고 하나의 Pod에서만 읽고 쓰기 가능
ReadWriteMany (RWX): 여러 개의 Pod에 마운트 가능하고 여러 개의 Pod에서 읽고 쓰기 가능
ReadOnlyMany (ROX): 여러 개의 Pod에 마운트 가능하고 여러 개의 Pod에서 읽기는 가능하지만 쓰기는 불가능
kubectl apply -f nfs-pvc.yaml

persistentvolumeclaim/nfs-pvc-test created
kubectl get pv,pvc
NAME CAPACITY ACCESS MODES RECLAIM POLICY STATUS CLAIM STORAGECLASS REASON AGE
persistentvolume/pvc-2dca7757-d8c1-4e80-8a21-f1d661d69b19   10Mi       RWX            Delete           Bound    default/nfs-pvc-test   managed-nfs-storage            7s

NAME STATUS VOLUME CAPACITY ACCESS MODES STORAGECLASS AGE
persistentvolumeclaim/nfs-pvc-test    Bound     pvc-2dca7757-d8c1-4e80-8a21-f1d661d69b19   10Mi       RWX            managed-nfs-storage   7s
sudo ls /data/NFS
default-nfs-pvc-test-pvc-2dca7757-d8c1-4e80-8a21-f1d661d69b19
apiVersion: apps/v1
kind: Deployment
metadata:
name: ccambo-nfs-test
  labels:
app: nginxnfs
spec:
replicas: 2
selector:
matchLabels:
app: nginxnfs
  template:
metadata:
labels:
app: nginxnfs
    spec:
containers:
- name: nginxnfs
        image: nginx:latest
        ports:
- containerPort: 80
volumeMounts:
- mountPath: /nfs
            name: nfsvolume
      volumes:
- name: nfsvolume
        persistentVolumeClaim:
claimName: nfs-pvc-test
kubectl apply -f nfs-test-app.yaml
deployment.apps/ccambo-nfs-test created
kubectl get deploy


NAME READY UP-TO-DATE AVAILABLE AGE
ccambo-nfs-test 0/1 1 0 15s
nfs-client-provisioner 1/1 1 1 75m
kubectl get pods
kubectl exec -it ccambo-nfs-test-9d7fc4c6c-25xr4 -- /bin/bash
cd /nfs
echo "This is NFS test" > /nfs/test.log
cat /nfs/test.log
This is NFS test
kubectl exec -it ccambo-nfs-test-9d7fc4c6c-js5pl -- /bin/bash
> ls /nfs
test.log


> cat /nfs/test.log
This is NFS test
|
|
안됐던 부분 |
되는 부분 |
|
|
kind: ClusterRole apiVersion: rbac.authorization.k8s.io/v1 metadata: name: nfs-provisioner-clusterRole rules: - apiGroups: [""] resources: ["persistentvolumes"] verbs: ["get", "list", "watch", "create", "delete"] - apiGroups: [""] resources: ["persistentvolumeclaims"] verbs: ["get", "list", "watch", "update"] - apiGroups: ["storage.k8s.io"] resources: ["storageclasses"] verbs: ["get", "list", "watch"] - apiGroups: [""] resources: ["events"] verbs: ["create", "update", "patch"] |
kind: ClusterRole apiVersion: rbac.authorization.k8s.io/v1 metadata: name: nfs-provisioner-runner rules: - apiGroups: [""] resources: ["persistentvolumes"] verbs: ["get", "list", "watch", "create", "delete"] - apiGroups: [""] resources: ["persistentvolumeclaims"] verbs: ["get", "list", "watch", "update"] - apiGroups: ["storage.k8s.io"] resources: ["storageclasses"] verbs: ["get", "list", "watch"] - apiGroups: [""] resources: ["events"] verbs: ["watch", "create", "update", "patch"] - apiGroups: [""] resources: ["services", "endpoints"] verbs: ["get"] - apiGroups: ["extensions"] resources: ["podsecuritypolicies"] resourceNames: ["nfs-provisioner"] verbs: ["use"] |