dnf -y install openstack-neutron-openvswitch libibverbs
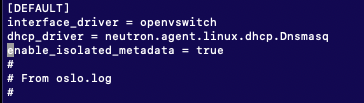
vi /etc/neutron/dhcp_agent.ini
[DEFAULT]
			interface_driver = openvswitch
			dhcp_driver = neutron.agent.linux.dhcp.Dnsmasq
			enable_isolated_metadata = true
vi /etc/neutron/l3_agent.ini
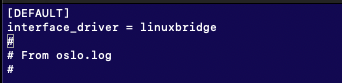
변경 전
interface_driver = openvswitch
dhcp_driver = neutron.agent.linux.dhcp.Dnsmasq
enable_isolated_metadata = true
vi /etc/neutron/plugins/ml2/ml2_conf.ini
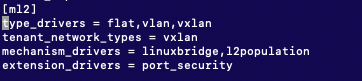
type_drivers = flat,vlan,gre,vxlan
tenant_network_types =
mechanism_drivers = openvswitch
vi /etc/neutron/plugins/ml2/openvswitch_agent.ini
[securitygroup]
			firewall_driver = openvswitch
			enable_security_group = true
			enable_ipset = true
vi /etc/nova/nova.conf
			use_neutron = True
			linuxnet_interface_driver = nova.network.linux_net.LinuxOVSInterfaceDriver
			firewall_driver = nova.virt.firewall.NoopFirewallDriver
su -s /bin/bash neutron -c "neutron-db-manage --config-file /etc/neutron/neutron.conf --config-file /etc/neutron/plugin.ini upgrade head"
systemctl enable openvswitch
systemctl restart openvswitch

systemctl restart neutron-server neutron-metadata-agent neutron-openvswitch-agent.service
systemctl restart openstack-nova-api
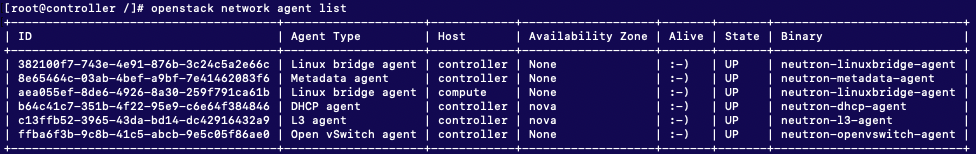
systemctl disable neutron-linuxbridge-agent.service
systemctl stop neutron-linuxbridge-agent.service
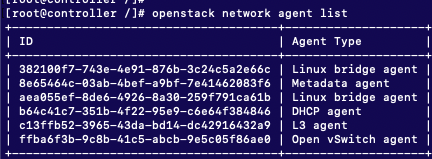
openstack network agent delete [확인한 ID]
dnf -y install openstack-neutron-openvswitch openstack-neutron-ml2
vi /etc/neutron/neutron.conf
core_plugin = ml2
service_plugins = router
state_path = /var/lib/neutron
allow_overlapping_ips = True
vi /etc/neutron/plugins/ml2/ml2_conf.ini
[ml2]
			type_drivers = flat,vlan,gre,vxlan
			tenant_network_types = vxlan

[ml2_type_flat]
			flat_networks = provider

[ml2_type_vxlan]
			vni_ranges = 1:1000
[securitygroup]
			firewall_driver = openvswitch
			enable_security_group = true
			enable_ipset = true
vi /etc/neutron/plugins/ml2/openvswitch_agent.ini
[agent]
			tunnel_types = vxlan
			prevent_arp_spoofing = True

[ovs]
			local_ip = [컴퓨트 노드 IP]
[securitygroup]
			firewall_driver = openvswitch
			enable_security_group = true
			enable_ipset = true
vi /etc/nova/nova.conf
use_neutron = True
linuxnet_interface_driver = nova.network.linux_net.LinuxOVSInterfaceDriver
firewall_driver = nova.virt.firewall.NoopFirewallDriver
systemctl enable openvswitch
systemctl restart openvswitch

systemctl enable neutron-openvswitch-agent
systemctl restart neutron-openvswitch-agent
systemctl restart openstack-nova-compute
	systemctl disable neutron-linuxbridge-agent.service
	systemctl stop neutron-linuxbridge-agent.service

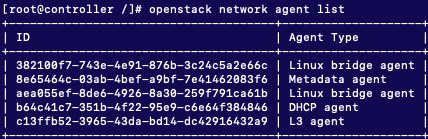
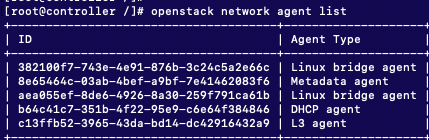
	openstack network agent list 명령어로 ID를 확인하고

	openstack network agent delete [확인한 ID]