SSL 취약점을 이용한 공격, Heart bleed(하트블리드) 실습
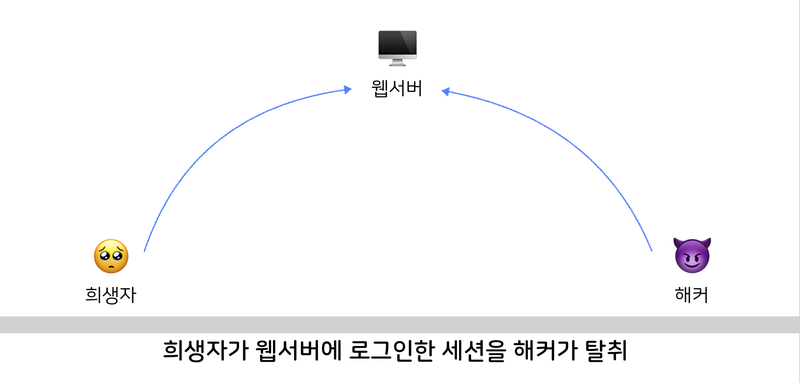
웹 세션 하이재킹
[ 이전 글 ]과 이어지는 웹 세션 하이재킹 Heart bleed 실습 입니다.
✅ 잠깐, Session Hijacking 이란?
서버와 클라이언트 사이에서 이루어지는 통신에 낑겨서 클라이언트가 서버로 붙어있는 세션을 탈취해오는 기술.
세션 하이재킹에 대한 글 : https://sudo-minz.tistory.com/72
제로보드 설치 (간단한 웹사이트 생성)
제로보드를 설치하기 위해,
php php-devel php-pear php-mysql php-mbstring php-gd php-imap php-odbc php-xmlrpc php-xml 등을 설치한다.
[root@localhost /]# yum install php php-devel php-pear php-mysql php-mbstring php-gd
php-imap php-odbc php-xmlrpc php-xml


Loaded plugins: fastestmirror, refresh-packagekit, security
Loading mirror speeds from cached hostfile
* base: centos.tt.co.kr
* extras: centos.tt.co.kr
* updates: centos.tt.co.kr
[ 생략 ]
제로보드를 설치하기 위해 mysql-server를 설치한다.
[root@localhost /]# yum install mysql-server
mysql에서 xe DB를 생성.
[root@localhost /]# mysql -u root -p

Enter password:
Welcome to the MySQL monitor. Commands end with ; or \g.
Your MySQL connection id is 4
Server version: 5.1.73 Source distribution

Copyright (c) 2000, 2013, Oracle and/or its affiliates. All rights reserved.

Oracle is a registered trademark of Oracle Corporation and/or its affiliates.
Other names may be trademarks of their respective owners.
Type 'help;' or '\h' for help. Type '\c' to clear the current input statement.

mysql> create database xe;
Query OK, 1 row affected (0.00 sec)

mysql> show databases; +-----------------------+
| Database | +-----------------------+
| information_schema |
| mysql |
| test |
| xe | +-----------------------+ 4 rows in set (0.00 sec)
php 설정파일을 다음과 같이 설정한다.
[root@localhost /]# vi /etc/php.ini

short_open_tag = On
allow_call_time_pass_reference = On
error_reporting = E_ALL & ~E_NOTICE & ~E_DEPRECATED & ~E_USER_DEPRECATED
display_errors = On
display_startup_errors = On
register_globals = On
register_long_arrays = Off
magic_quotes_gpc = On
magic_quotes_runtime = Off
date.timezone = "Asia/Seoul"
아파치 설정 파일에 굵은 글씨 부분을 추가한다.
[root@localhost /]# vi /etc/httpd/conf/httpd.conf
AddType application/x-httpd-php .php .php3 .php4 .php5 .html .htm .inc
DirectoryIndex index.html index.htm index.php
[root@localhost /]# service httpd restart
제로보드를 다운 받아 압축을 풀고 디렉토리의 권한을 707로 변경해준다.
[root@localhost /]# chmod 707 /var/www/html/xe
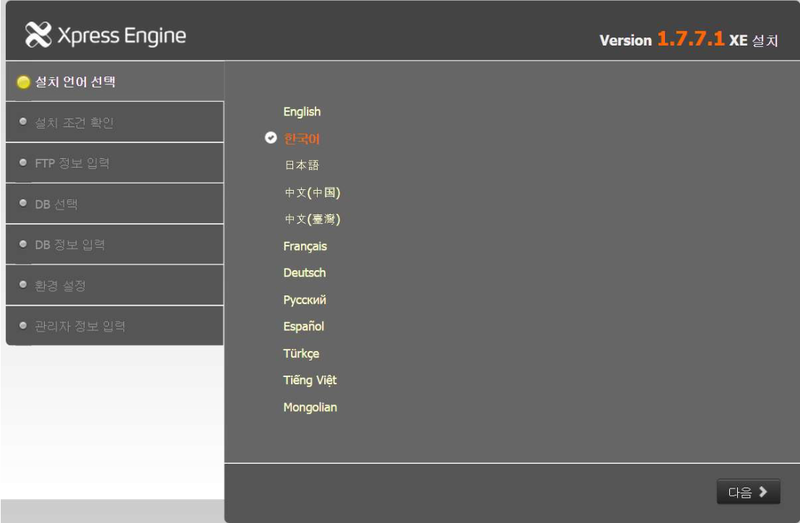
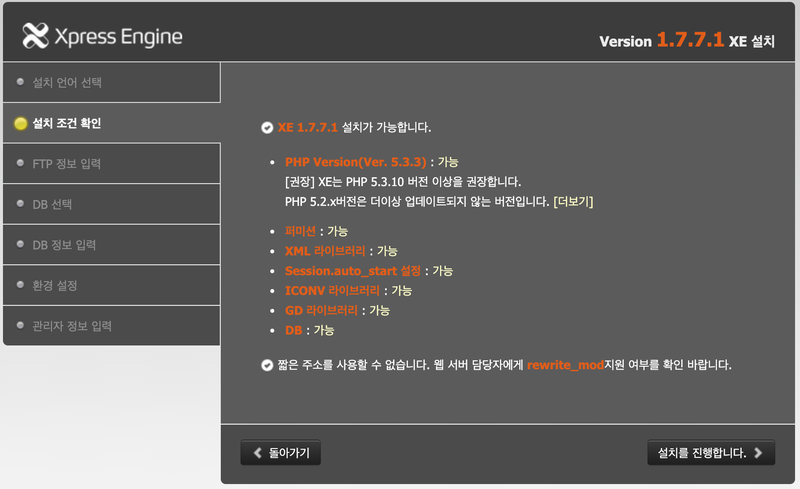
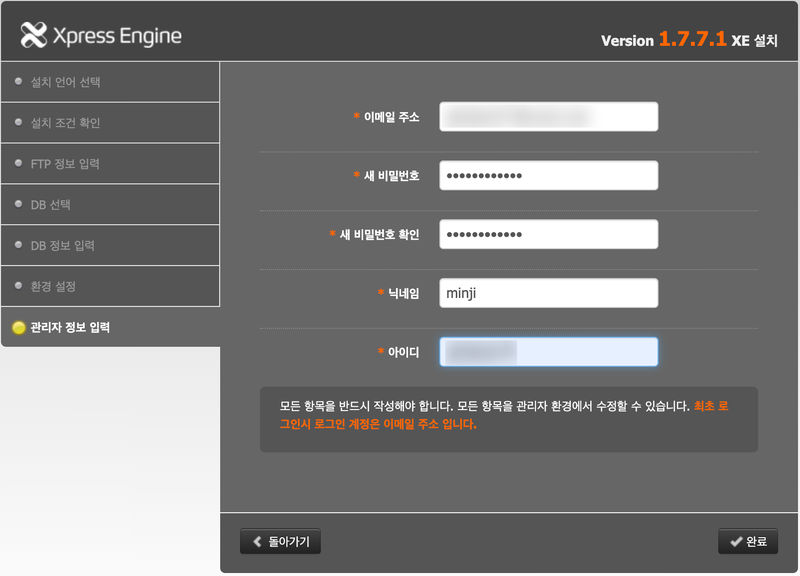
웹 브라우저로 접속해 설치를 진행
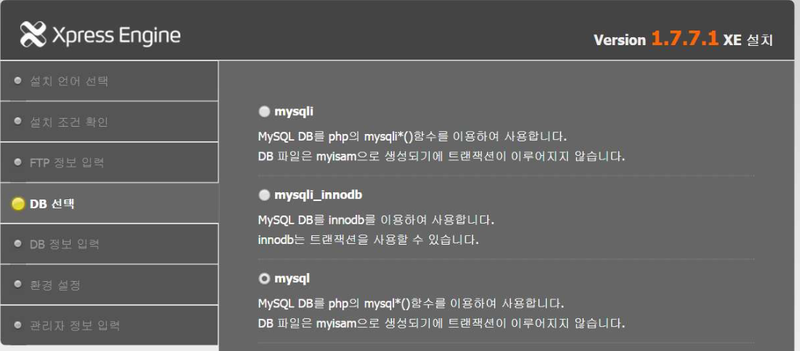
mysql을 체크하고 다음으로 넘어간다.
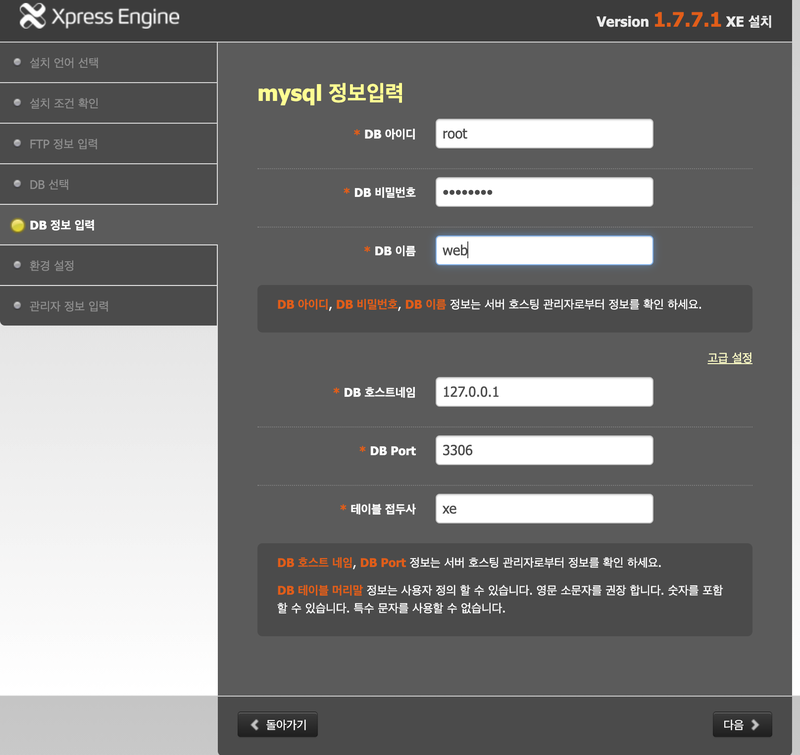
2.
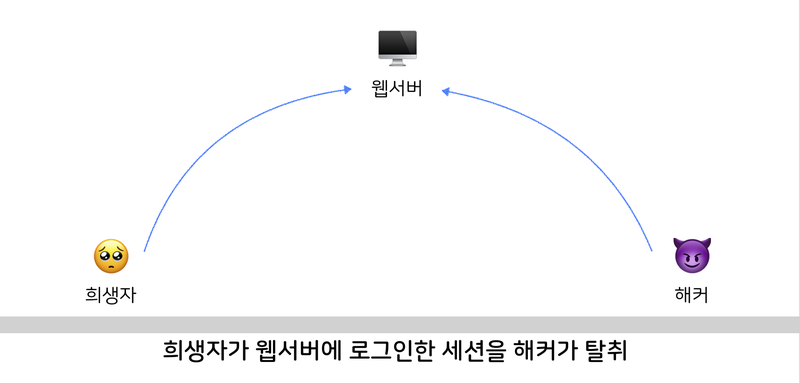
희생자와 해커가 웹사이트에 각 계정으로 로그인.
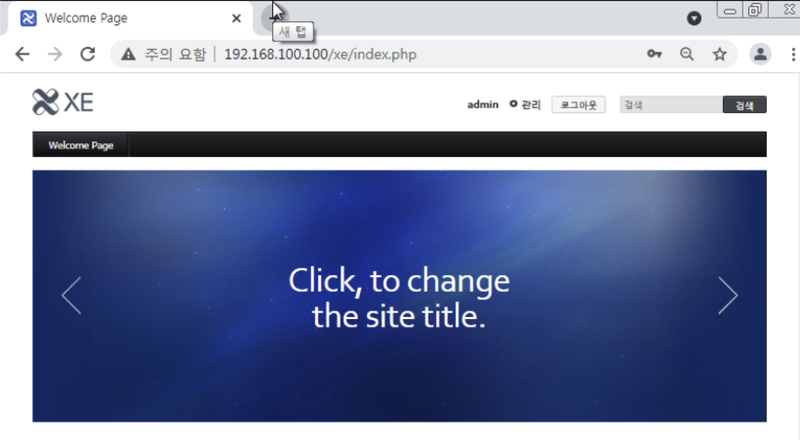
admin 관리자
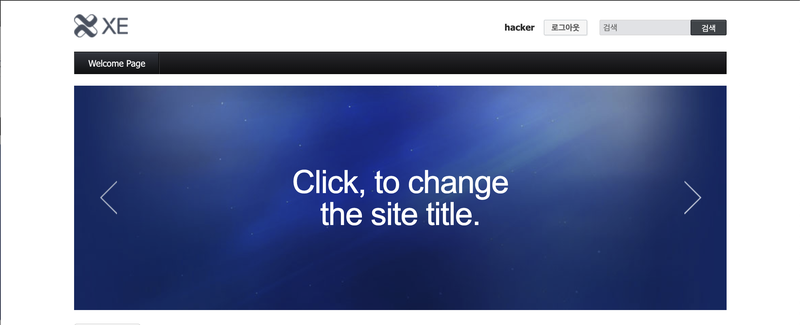
일반 유저 : 해커
해커쪽에서 edit this cookie 확장 프로그램을 다운 받는다.
그리고 해커 쪽에서 취약한 환경인 웹서버로 heart bleed 공격.

내용을 확인해보면
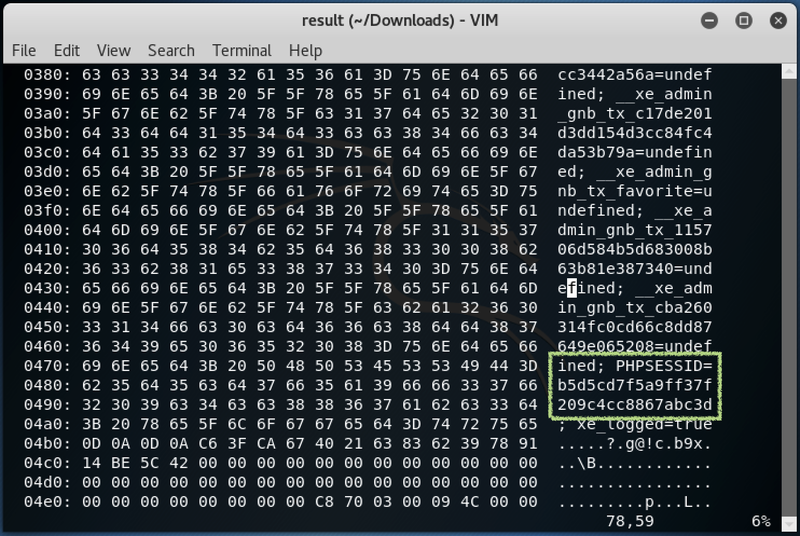
이렇게 관리자 로그인 세션 ID가 보인다.
이것을 이용해 해커가 관리자로 로그인 할 수 있다.
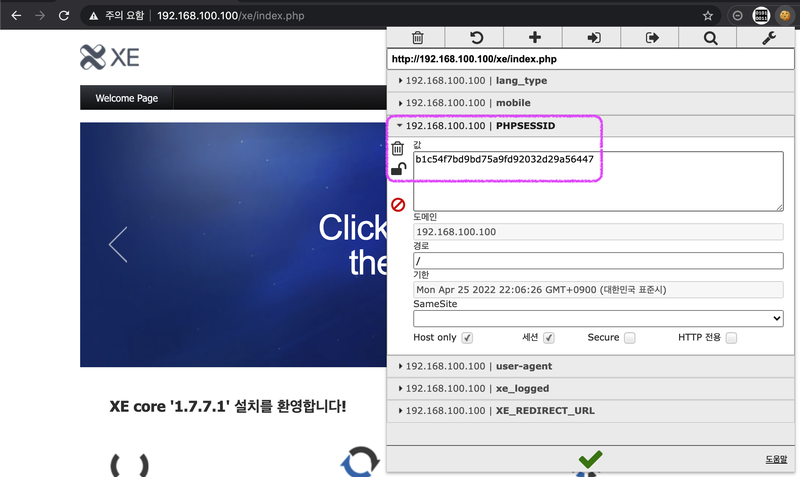
이렇게 된다면 해커가 마음대로 사이트의 글을 생성 및 수정 삭제 등이 가능해진다.
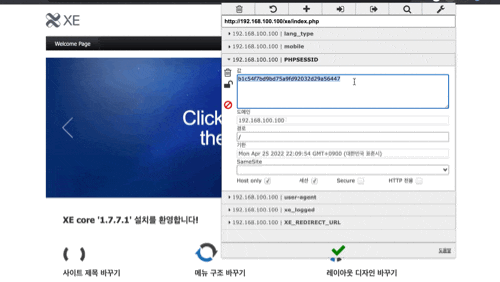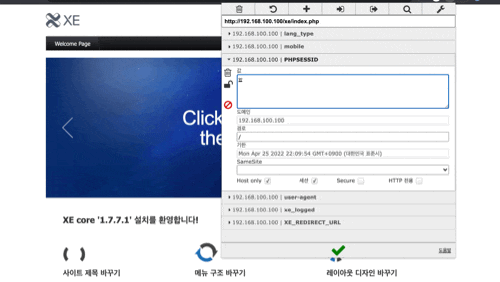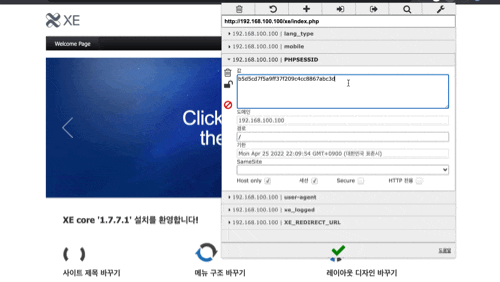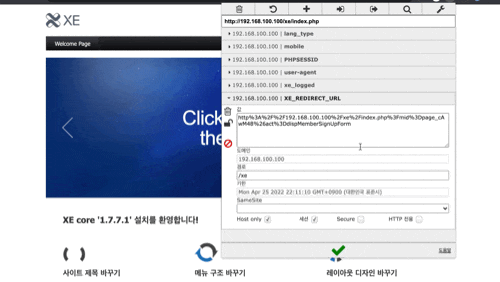
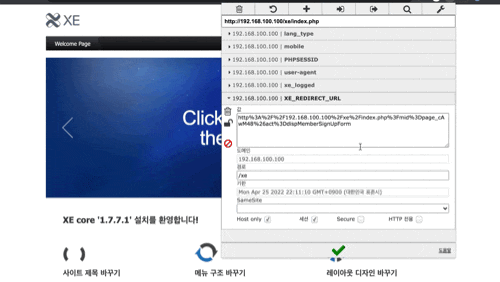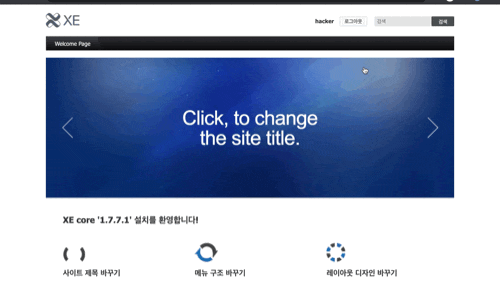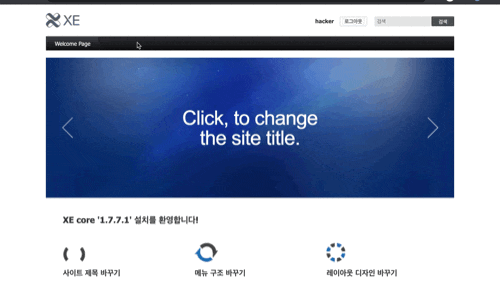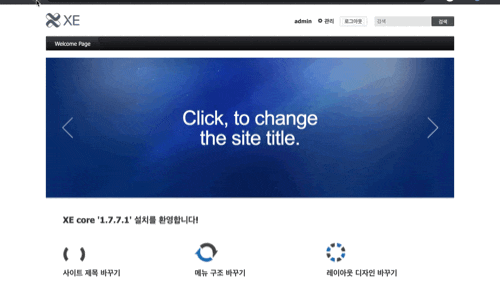
해커의 세션 아이디를 관리자 세션 아이디로 바꾸고 저장.
그리고 사이트 새로고침을 하면, 이렇게 관리자로 로그인 된다.